Audit Trails for AI Agents: Record Intent, Execution and Uncertainty
Build an audit trail that separates approved intent from external outcomes, survives retries and helps reconstruct what happened without claiming automatic compliance.
Ostap Kovalisko
Founder & AI Systems Architect
Updated 2026-10-18 · Sources and technical review
In this article · 6 min
The worker times out. The interface says “failed.” Someone clicks retry. Later, you discover two records in the external system. An application log can tell you that two requests happened. A useful audit trail explains what was intended, what was approved and what is actually known about each attempt.
That distinction matters more than collecting a large volume of logs. I want to be able to reconstruct an action without having to trust the final status label or the model’s explanation of its own behavior.
Separate intent from outcome
Give a logical action a stable identity. Give each attempt its own identity. Record the proposal version, target, payload reference, approval and applicable policy version. Then record the external response or the fact that a conclusive response never arrived.
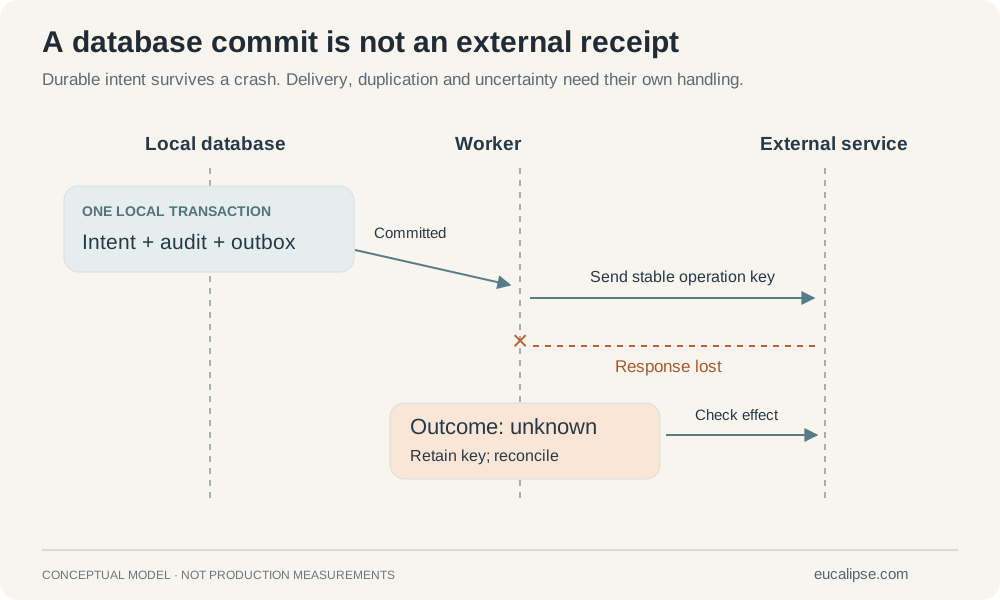
“Unknown” is a useful outcome. It says the system cannot yet tell whether the external effect occurred. Do not collapse it into “failed” if that label will invite an unsafe retry. Keep reconciliation events attached to the same logical action.
Be precise about the transaction boundary
A local database update, audit event and outbox item can commit in one transaction when they share that database. A separate worker delivers the committed intent to an external service. That service’s side effect does not become part of the local transaction.
AWS’s transactional outbox guide explains the dual-write problem and the need to handle duplicate delivery. An outbox makes intent durable. It does not grant exactly-once behavior to every API you call.
Use provider-supported idempotency where available, and keep the logical operation key stable across eligible retries. Stripe’s documentation is a concrete example of why the provider’s exact rules matter. Save receipts and external identifiers; reconcile ambiguous outcomes before assuming that no effect occurred.
Record evidence without collecting everything
The record should contain enough information to explain the decision and reproduce the relevant inputs under your retention policy. That does not mean copying every document, secret or personal detail into a permanent log. References to controlled versions can be more appropriate than duplicated raw content.
- Proposal: version, target, intended changes and evidence references.
- Decision: reviewer or policy identity, time, scope and any edits.
- Attempt: worker identity, idempotency key, timestamps and response classification.
- Outcome: confirmed effect, confirmed failure or uncertainty awaiting reconciliation.
- Correction: a new event identifying what it supersedes and why.
Append-only application events are useful for reconstruction, but they do not by themselves make storage tamper-proof. Access controls, retention, deletion policy, monitoring and the storage threat model need separate design. An audit trail supports review; it does not by itself establish regulatory compliance.
Do not confuse a rationale with a trace
A model-generated explanation can help a reviewer understand a proposal. It is not a faithful record of every internal computation. Label it as a stated rationale and preserve the actual inputs, tool calls, policy checks and observed results needed to evaluate it.
Likewise, an approval is evidence that someone accepted a proposal, not an independently verified correctness label. If audit events become evaluation examples, add an explicit adjudication step. Agent actions under retries explores the execution side of this distinction.
Test the reconstruction, not just the logging call
Pick a deliberately interrupted action and trace it from proposal to final reconciliation. Can you identify which version was approved? Can you distinguish a retry from a new task? Can you explain an unknown outcome without inventing a success or failure? That exercise finds gaps a green logging dashboard will miss.
Frequently asked questions
Can an external action and its audit record share a database transaction?+
A local transaction can atomically store intent and an outbox event. An external API effect happens separately and needs delivery, idempotency and reconciliation handling.
Does append-only logging guarantee compliance?+
No. Audit records are one control. Retention, access, data handling and applicable obligations require separate assessment.
Why keep an unknown outcome?+
A timeout can occur after an external effect succeeds. Recording uncertainty prevents the system from assuming it is safe to repeat the action.
Let's Talk About Your Project
Have questions about nearshoring or AI development? Our team is here to help you make the right decision.
- ✓Free consultation on your AI project
- ✓Custom cost estimates and timeline
- ✓Access to nearshore talent pools